
Securing RAG and AI Agents

AI SECURITY · BLOG 09 Securing RAG and AI Agents Part 4 of the KIS AI Security Series: a practical guide to retrieval-augmented generation security, AI agent permissions, access control and monitoring for enterprise AI. AI Security Series · Part 48 min readFor product, security & engineering teams RAG & AGENT SECURITY STARTERGround the answer. […]
When Content Fights Back
AI SECURITY · BLOG 08 When Content Fights Back Part 3 of the KIS AI Security Series: recognise prompt injection in documents, websites and messages, then contain it with controls that work outside the model. AI Security Series · Part 37 min readFor product, security & engineering teams PROMPT INJECTION STARTERSeparate instructions from evidence. 01SpotFind […]
Protecting Data in AI Workflows

AI SECURITY · BLOG 07 Protecting Data in AI Workflows Part 2 of the KIS AI Security Series: keep sensitive information in the right hands as prompts, documents and model outputs move through an AI-enabled service. AI Security Series · Part 26 min readFor business & security teams DATA PROTECTION STARTERKnow the data. Bound the […]
AI Security Foundations
A practical introduction to the risks, controls and operating model every organisation needs before scaling AI.
AI Security with Human Oversight
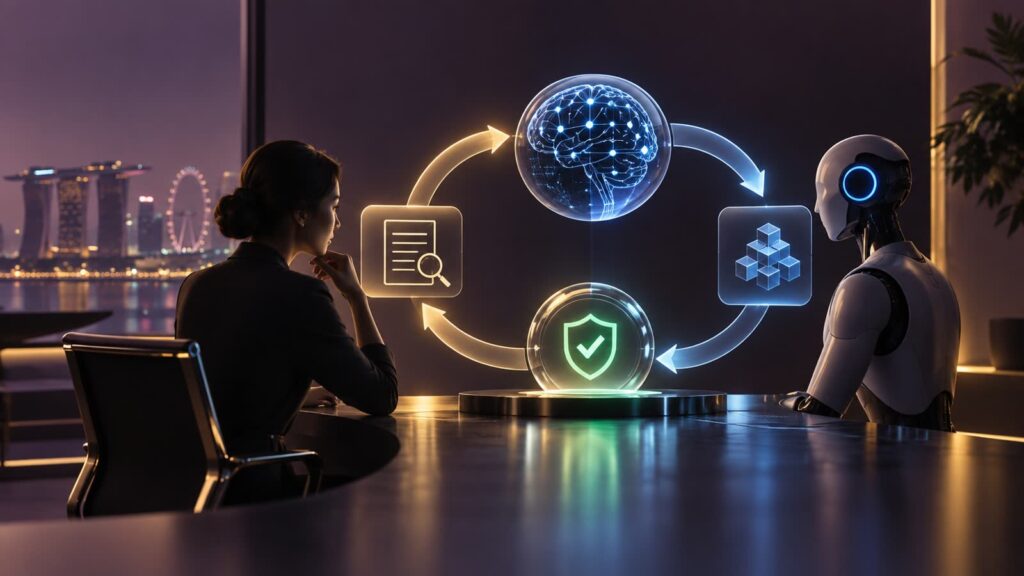
AI SECURITY · BLOG 05 AI security with human oversight A practical playbook for governing AI use, managing model risk and protecting data without slowing responsible innovation. AI Security6 min readFor risk, product & technology leaders RESPONSIBLE AI LOOPUnderstand it. Control it. Assure it. 01DiscoverMap models, vendors, data and business decisions. 02ClassifyRate impact, sensitivity and […]
Cloud Security by Design

SECURITY & CLOUD IMPLEMENTATION · BLOG 04 Cloud security by design A practical guide to building secure Azure and AWS foundations, from identity and configuration to telemetry that helps teams act early. Cloud Security7 min readFor cloud & platform leaders CLOUD CONTROL LOOPDesign it. Observe it. Prove it. 01MapInventory accounts, subscriptions, workloads and data flows. […]
From Alert Fatigue to Confident Response
MANAGED SECURITY VIA SOC · BLOG 03 From alert fatigue to confident response A practical guide to building a security operations capability that turns noisy signals into timely, explainable decisions. Managed Security6 min readFor security & operations leaders SOC SIGNAL LOOPSee it. Decide it. Improve it. 01CollectBring cloud, endpoint, identity and application signals together. 02CorrelateConnect […]
Finding the Break Before Attackers Do: A Practical VAPT, WAPT & Source Code Assurance Guide

SECURITY ASSURANCE & TESTING · BLOG 02 Finding the break before attackers do A practical guide to VAPT, WAPT, security control reviews and source code assurance that turns findings into safer releases. 9 min readFor product, engineering & security teamsSingapore ASSURANCE LOOPTest what matters. Fix what counts. 01ScopeAssets, users, trust boundaries and rules of engagement […]
From Cyber Risk to Cyber Trust: A Practical CTM & ISO/IEC 27001 Readiness Guide
CONSULTANCY & COMPLIANCE · BLOG 01 From cyber risk to cyber trust A practical guide to preparing for Singapore’s Cyber Trust Mark and building an ISO/IEC 27001:2022-ready information security management system. 8 min readFor founders, risk owners & security leadersSingapore READINESS MAPFrom obligation to evidence 01UnderstandBusiness context, scope and obligations 02PrioritiseRisk scenarios and material gaps […]
Hello world!
Welcome to WordPress. This is your first post. Edit or delete it, then start writing!