
Description
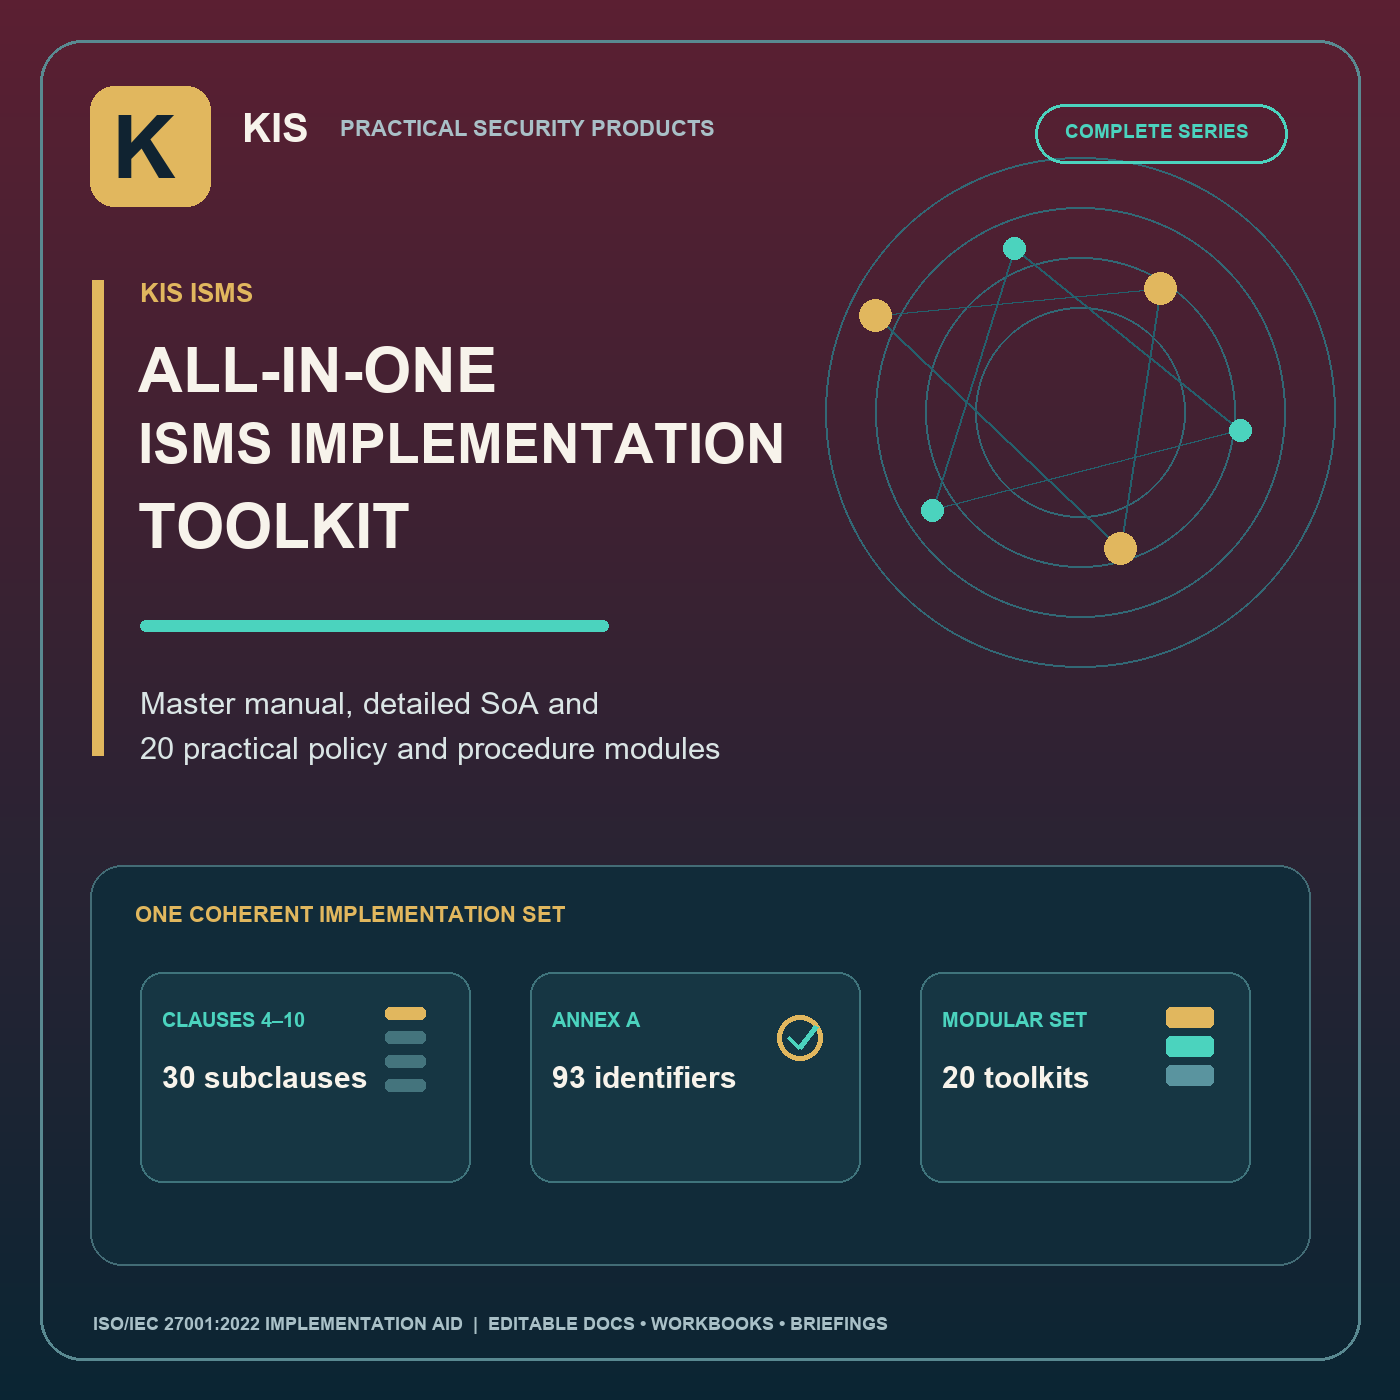
One coordinated implementation package: an ISMS master manual, detailed Statement of Applicability and 20 focused policy and procedure modules. Use the master manual as the governing framework. Tailor and reconcile each subordinate module to your approved scope, risks, responsibilities and actual controls.
Master materials
- ISMS Manual and Implementation Guide (Word + PDF): clause-by-clause implementation guidance for clauses 4–10, including organizational context and scope, leadership, policy, roles, risk planning, support, operation, performance evaluation, internal audit, management review and continual improvement. It includes steering committee and management responsibilities, decision points, evidence expectations, governance records, and appendices to help organize implementation.
- Working Registers and detailed SoA (Excel): a clause map and a working Statement of Applicability covering all 93 Annex A identifiers, with applicability, rationale, implementation state, owner and evidence fields. It also includes risk, policy, data-flow, audit and action registers.
All 20 subordinate module toolkits
Each module includes an editable Word policy/procedure, matching PDF, editable PowerPoint briefing and Excel workbook. The sequence moves from governance, context, risk and the SoA through asset, access, people, supplier, physical and technical controls, incident handling, privacy, secure change, internal audit, management review, and corrective action. Every module also has its own readme. The download includes one complete ZIP and a second ZIP containing the 20 standalone module bundles.
Suggested implementation sequence
- Agree scope, context, interested parties, obligations, executive sponsorship and accountable owners.
- Approve the risk method, assess information-security risks and select treatment.
- Complete the SoA with a reasoned applicability decision for every Annex A identifier; assign owners and evidence.
- Tailor the subordinate procedures to the master manual and implement approved controls.
- Retain operating records, evaluate results, conduct independent internal audit and hold management review.
- Track nonconformities and actions to a documented effectiveness decision.
Quality and reference boundary
The package contains original KIS guidance and identifiers. It does not reproduce ISO standard text, certify an organization or determine an auditor’s conclusion. Applicable controls and conformity depend on the organization’s scope, risk treatment, obligations, operation and evidence. Verify the materials against a licensed copy of ISO/IEC 27001:2022 and applicable amendments.
Important: This package is not legal advice, an audit opinion or a certification guarantee. Validate legal and contractual obligations for your organization and adapt each template before use. KIS is not affiliated with or endorsed by ISO or IEC.
Reviews
There are no reviews yet.