
Description
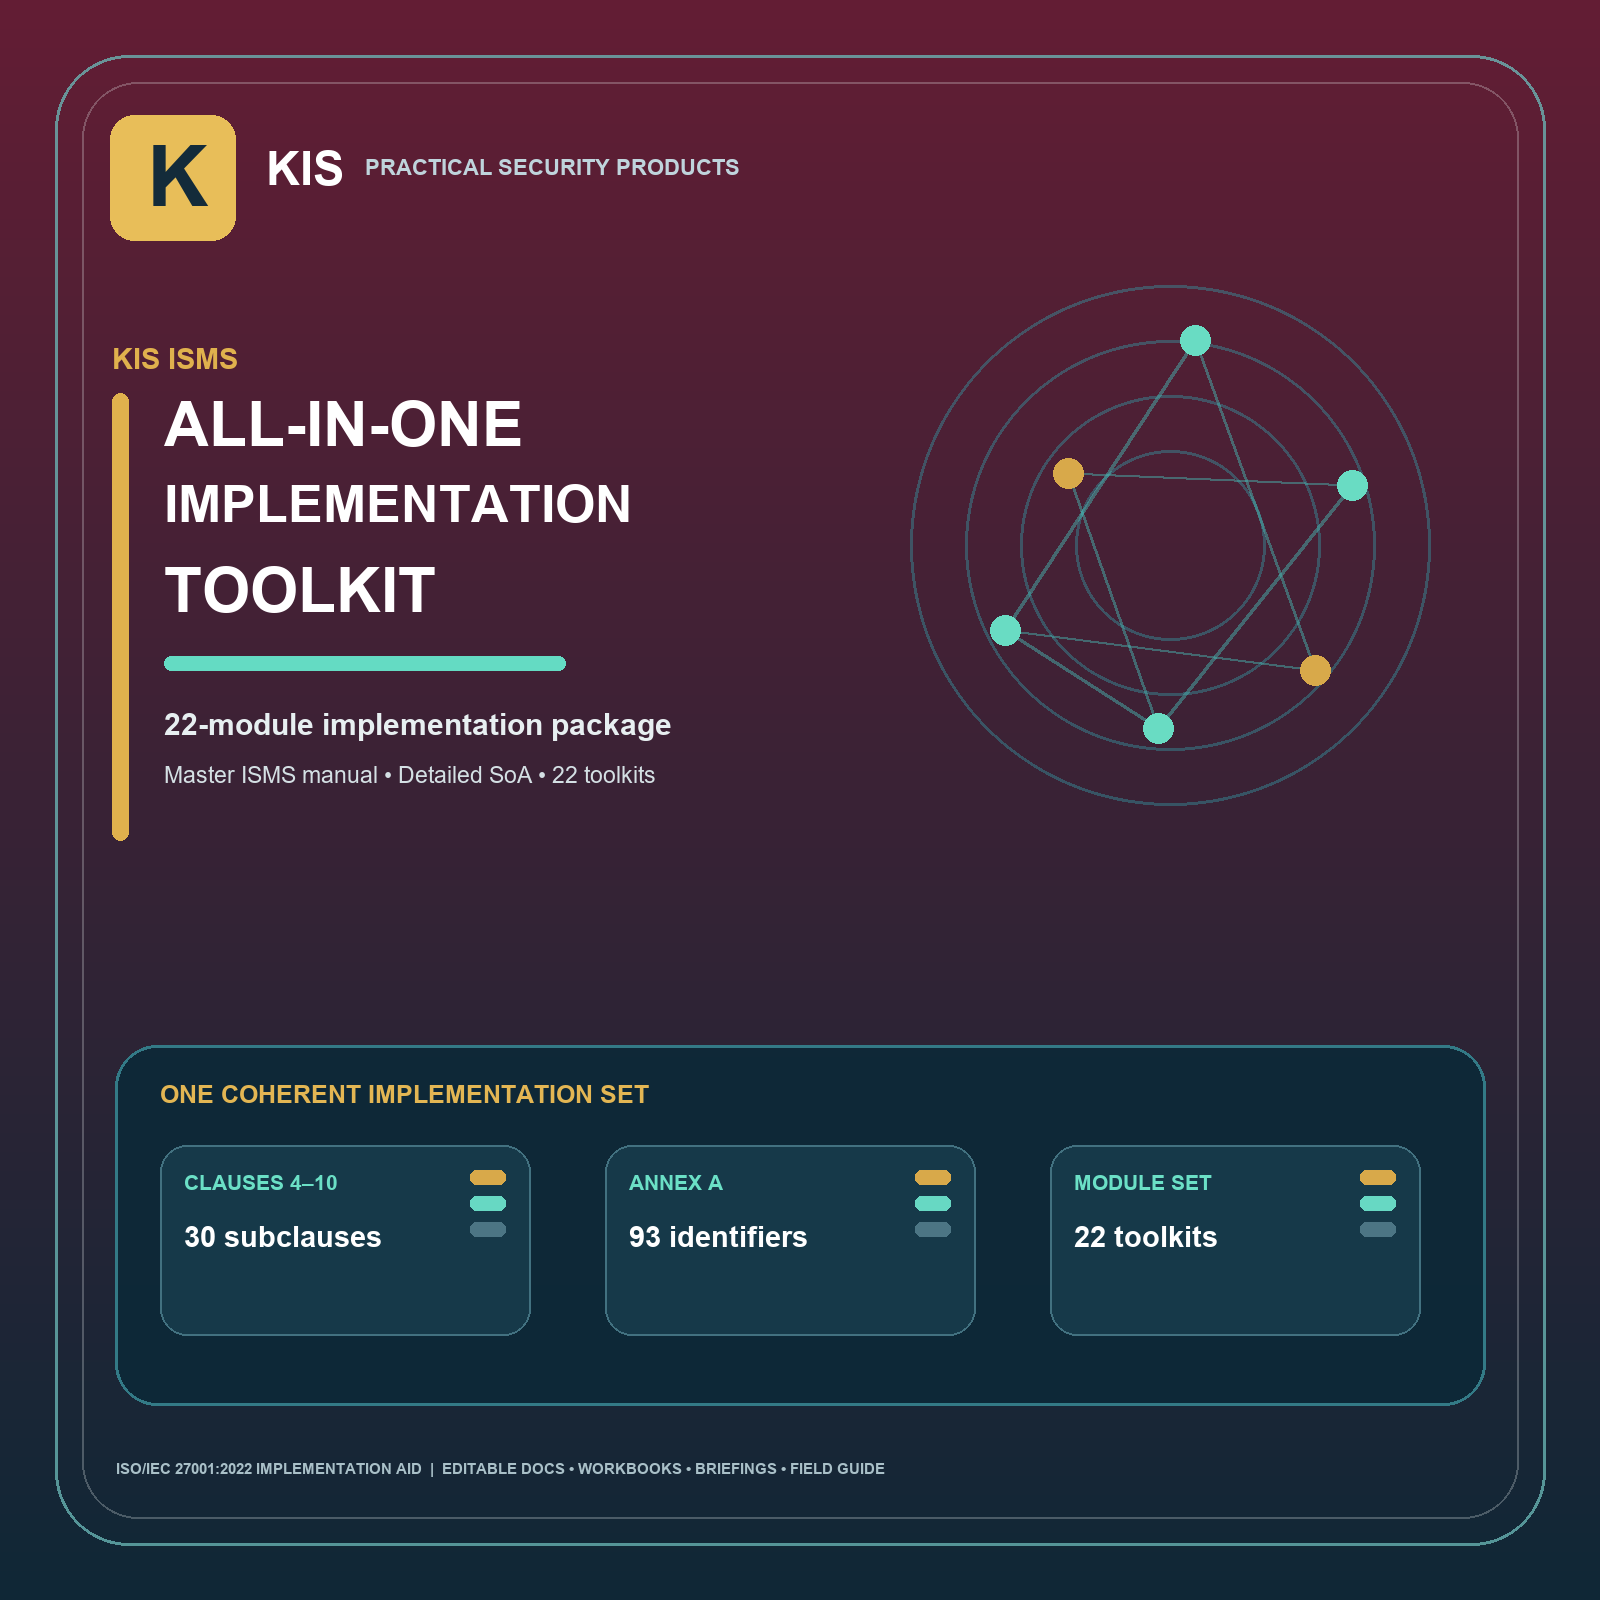
A coordinated implementation and lifecycle toolkit for building, operating, reviewing and improving an information security management system. This release contains 22 numbered ISMS modules. Modules 01–20 form the core implementation set; Modules 21–22 support certification readiness, auditor evidence and ongoing surveillance and improvement.
Download the free 17-page “How to Use the KIS ISMS 22-Module Toolkit” guide (PDF) — available without checkout.
Master implementation materials
- Master ISMS Manual and Implementation Guide (Word and PDF): a governing framework for clauses 4–10, with clause and subclause guidance, leadership and management steering responsibilities, scope and obligation decisions, risk planning, operating responsibilities, performance evaluation, internal audit, management review and improvement. Use it as the parent document and align subordinate procedures with approved organizational decisions.
- Working Registers and detailed SoA (Excel): a clause map, a working Statement of Applicability with a decision prompt for each of the 93 Annex A control identifiers, and risk, policy, data-flow, audit and corrective-action registers. Applicability and implementation status must be determined from your organization’s scope, risks, obligations and evidence.
22 coordinated module toolkits
- Modules 01–20 — Core implementation: governance, context and scope, risk method and treatment, objectives, documented information, assets, access, people, suppliers, physical security, operations, cryptography, continuity, incidents, privacy and data sovereignty, secure development and change, internal audit, management review, and corrective action.
- Module 21 — Certification Readiness and Auditor Evidence: organize scope, evidence, interviews, sampling, readiness gaps and ownership before an external assessment.
- Module 22 — Surveillance and Continual Improvement: plan recurring reviews, change triggers, performance trends and improvement actions during ongoing operation.
The main ZIP contains all 22 numbered module folders and their released working files. A separate ZIP contains the 22 standalone module bundles. The two lifecycle modules complement the core system; they do not replace it or predict a certification body’s decision.
Module 01–15 refresh in Release 1.2.0
Modules 01–15 now include expanded module-specific Word and PDF implementation guides, practical five-tab workbooks with decision and evidence registers plus working indicator and due-date formulas, eight-slide editable briefings, fictional worked examples, reviewer evidence tests and 30-day adoption checklists. Modules 16–22 remain in their published releases. Replace all sample roles, dates and target values before operational use.
How to work through the package
- Set sponsorship, scope, context, interested parties, obligations and accountable roles.
- Approve the risk method; assess risks and select treatment.
- Complete and approve the SoA, recording reasoned applicability decisions, owners and evidence.
- Tailor subordinate procedures to the master manual, then authorize, communicate and operate them.
- Collect and test operating evidence, measure performance and conduct impartial internal audit.
- Use management review to decide priorities, resources and changes; track corrective actions through effectiveness review.
- Use Modules 21–22 for external-audit readiness and the continuing surveillance and improvement cycle.
Product count clarification
The KIS shop currently displays 24 product listings: 22 standalone numbered ISMS modules, this all-in-one package, and a separate SME Incident Readiness Kit. The catalog count is 24 products; this bundle contains 22 numbered ISMS modules.
Reference and assurance boundaries
This package contains original KIS implementation guidance and does not reproduce ISO standard text. It is not legal advice, an audit opinion, a conformity assessment or a certification guarantee. Verify current requirements in a licensed copy of ISO/IEC 27001:2022, including applicable amendments; validate laws and contracts; and tailor, approve, communicate and test the materials against actual operations. KIS is not affiliated with or endorsed by ISO or IEC. Certification decisions are made independently by the certification body.


Reviews
There are no reviews yet.